Companies and software referenced
Each company links to an official product page or primary source relevant to this guide. Monogram tiles identify the referenced organisation and do not imply endorsement.
A practical cybersecurity lead generation agency shortlist includes Callbox, Martal Group, SalesHive, CyberTheory and Provena. Callbox publishes a dedicated multichannel cybersecurity programme. Martal combines outsourced security prospecting and appointment setting. SalesHive centres United States SDR calling and email. CyberTheory builds cybersecurity demand through paid, media, account based and intent programmes. Provena connects account research, verified data, cold email, LinkedIn, organic content, conversion and reply qualification. Choose by the missing function, security buyer, evidence standard and sales accepted result.
Which cybersecurity lead generation agency fits the actual growth constraint?
Cybersecurity vendors sell into a market where buyers are trained to question claims and inspect supplier risk. A generic message can fail even when the target title is correct. The agency brief must identify the security category, deployment environment, accountable workflow, buying group, evidence owner and next commercial commitment. The answer must fit the buyer, the people doing the work and the evidence available after launch. A fashionable platform or generic checklist cannot repair weak targeting or unclear ownership.
Choose one immediate constraint. A company that needs category trust and sustained market visibility should not buy a calendar only service. A company that already has credible proof and a finite account universe may need direct outbound and qualification rather than a broad paid programme. Compare every provider against the same constraint and accepted pipeline definition. Write the desired business outcome first, then define what must be true for it to occur and which risks require a human decision.
Which criteria matter when assessing cybersecurity lead generation agencies?
We reviewed current official provider service material on 28 August 2026. Inclusion required a published cybersecurity or security delivery route, a clear lead generation, appointment setting or demand generation boundary and enough first party detail to distinguish the operating model. We did not use paid rankings, affiliate links, universal scores or unattributed performance claims. For cybersecurity lead generation agencies, we used documented capability and practical fit. No paid placement, invented scores or unsupported performance claims were used. Check current pricing and packaging directly.
| Choice | Best fit | Core strength | Main tradeoff |
|---|---|---|---|
| Callbox | cybersecurity companies seeking a dedicated global multichannel lead generation and appointment setting programme | published cybersecurity positioning across account targeting, voice, email, LinkedIn, content, events and qualified meetings | the broad service and geographic boundary requires verification of the named team, market, claim review and comparable evidence |
| Martal Group | security software, managed service and related companies seeking outsourced prospecting and omnichannel appointment setting | a published security service spanning profile definition, contact sourcing, email, LinkedIn, phone, qualification and meeting booking | the service page covers physical and cybersecurity companies, so the proposal must prove the assigned team understands the exact category |
| SalesHive | United States cybersecurity teams prioritising a dedicated SDR motion across phone and email | published cybersecurity buyer coverage across security, information technology, operations, identity, risk and compliance roles | its public operating model centres direct sales development rather than a complete organic content, public relations or paid demand programme |
| CyberTheory | cybersecurity companies whose main constraint is market visibility, credibility and demand before direct sales engagement | cybersecurity specific demand generation across paid search, programmatic media, public relations, paid social, account based campaigns, events and intent signals | a demand creation and capture programme is a different purchase from an outsourced SDR team or a narrow appointment setting test |
| Provena | vertical B2B cybersecurity vendors needing a finite account market, verified contacts, direct outreach, organic content and qualification in one learning loop | one operating boundary across research, data, cold email, LinkedIn, content, conversion pages, reply qualification and pipeline review | Provena has no published cybersecurity specific client case study and is not a security assessor, compliance consultant, managed security provider or full paid media department |
What should a cybersecurity company verify before choosing a growth agency?
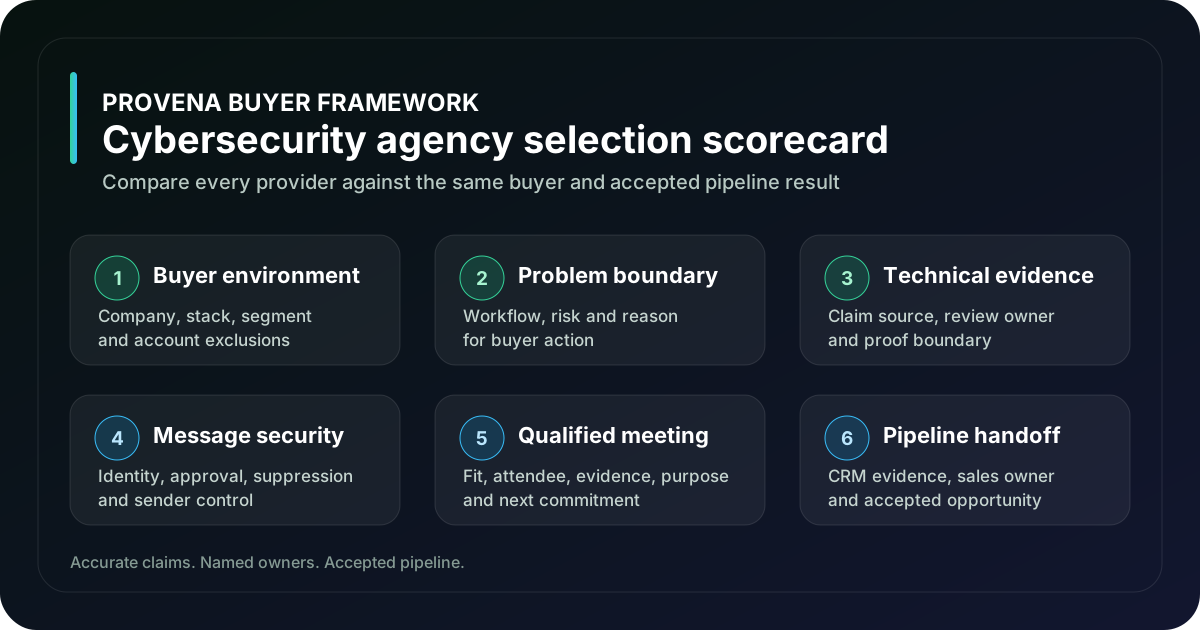
Provena publishes this comparison and sells a service included in it, so there is a direct commercial conflict. We do not name an overall winner. Provider scope comes from each company's official material. Fit, tradeoff and the six control scorecard are Provena editorial analysis.
The adjacent buyer tasks stay separate. The B2B lead generation agency comparison covers the wider provider market. The B2B SaaS demand generation agency comparison covers multi channel demand across software categories. This page adds the security buyer, technical evidence and trust boundary.
The NIST Cybersecurity Framework describes high level cybersecurity outcomes and adds governance as a core function. A growth agency does not certify product security or decide whether a buyer should accept supplier risk. It should preserve accurate product boundaries, source evidence and the named route to technical review.
The FTC states that commercial email has no business to business exception under the CAN SPAM Act and that a company cannot contract away responsibility for email sent on its behalf. Google also publishes authentication and sending requirements. Treat legal scope, sender controls and technical claims as named responsibilities supported by qualified owners, not as generic agency assurances.
Which cybersecurity lead generation agencies deserve a practical test?
Callbox: where does it fit?
Callbox publishes a dedicated cybersecurity service for areas including identity, cloud security, managed security, risk and compliance. Its material describes account based targeting and multichannel engagement. Ask for the exact security segment, buyer roles, evidence used in messages, delivery region and sales acceptance record for the proposed programme. Suits cybersecurity companies seeking a dedicated global multichannel lead generation and appointment setting programme. Strongest where published cybersecurity positioning across account targeting, voice, email, LinkedIn, content, events and qualified meetings matters. Test that the broad service and geographic boundary requires verification of the named team, market, claim review and comparable evidence.
Martal Group: where does it fit?
Martal presents a security lead generation service across cybersecurity platforms, managed security, cloud software and other security markets. Require a sourced account sample, message review route, named sales staff, qualification questions and CRM handoff. Provider claims about databases, intent and output remain provider attributed and should be tested in the selected market. Suits security software, managed service and related companies seeking outsourced prospecting and omnichannel appointment setting. Strongest where a published security service spanning profile definition, contact sourcing, email, LinkedIn, phone, qualification and meeting booking matters. Test that the service page covers physical and cybersecurity companies, so the proposal must prove the assigned team understands the exact category.
SalesHive: where does it fit?
SalesHive publishes a cybersecurity route using targeted lists, personalised email and cold calling by United States based SDRs. Its page names several security and technology decision makers and describes parallel contact across the buying group. Buyers should inspect the sample list, technical message, call recording policy, meeting acceptance rule and sales handoff. Suits united States cybersecurity teams prioritising a dedicated SDR motion across phone and email. Strongest where published cybersecurity buyer coverage across security, information technology, operations, identity, risk and compliance roles matters. Test that its public operating model centres direct sales development rather than a complete organic content, public relations or paid demand programme.
CyberTheory: where does it fit?
CyberTheory describes cybersecurity demand generation that builds awareness and consideration, then uses engagement and intent signals to guide capture. This can fit a crowded enterprise category with long independent research. Confirm channel budget, media ownership, content rights, source access, attribution rules and the point at which rising intent becomes a sales action. Suits cybersecurity companies whose main constraint is market visibility, credibility and demand before direct sales engagement. Strongest where cybersecurity specific demand generation across paid search, programmatic media, public relations, paid social, account based campaigns, events and intent signals matters. Test that a demand creation and capture programme is a different purchase from an outsourced SDR team or a narrow appointment setting test.
Provena: where does it fit?
Provena is our own service, so this is a disclosed vendor statement. The model fits a company with a defensible product boundary, a definable commercial buyer and a sales owner ready to handle qualified conversations and technical review. Adjacent vertical SaaS case material illustrates the operating method and does not forecast a cybersecurity outcome. Suits vertical B2B cybersecurity vendors needing a finite account market, verified contacts, direct outreach, organic content and qualification in one learning loop. Strongest where one operating boundary across research, data, cold email, LinkedIn, content, conversion pages, reply qualification and pipeline review matters. Test that provena has no published cybersecurity specific client case study and is not a security assessor, compliance consultant, managed security provider or full paid media department.
Which security buyer does each outreach channel actually reach?
Cybersecurity buying groups are wide, and each role answers a different channel. Match the channel to the person who can start an evaluation, not to the person who is easiest to find.
| Role | What they own | Channel that usually works | What earns a reply |
|---|---|---|---|
| CISO or head of security | Risk, budget and vendor consolidation | Peer referral, targeted email, events | A specific risk framing and evidence from a similar organisation |
| Security engineering lead | Tooling, integrations and alert load | LinkedIn, technical content, community | Technical depth and an honest integration story |
| IT or infrastructure director | Endpoints, identity and operations | Email and phone | Operational relief and a clear implementation path |
| Compliance or GRC owner | Frameworks, audits and evidence | Email, webinars, content | Mapping to the framework they report against |
| Managed service provider | Their clients' security stack | Partner outreach, phone | Margin, multi tenant fit and support |
Brief the agency on one or two of these roles per campaign. A message written for the CISO reads as noise to the engineer, and the reverse is also true.
How should a team introduce its chosen approach to cybersecurity lead generation agencies?
Test cybersecurity lead generation agencies against a representative workflow before committing. First test: Define the security category, deployment model, company segment, current environment, excluded accounts and accountable commercial buyer. Include ordinary records, difficult exceptions and the people who will own the system after selection.
- Define the security category, deployment model, company segment, current environment, excluded accounts and accountable commercial buyer.
- Map the user, security leader, information technology owner, risk, compliance, privacy, procurement, finance and executive roles that can influence the purchase.
- Give every provider the same product boundary, approved claims, source evidence, market exclusions, sales capacity and accepted outcome.
- Require a dated account sample showing why each company fits and which source supports every material targeting assumption.
- Name the product, security, legal and commercial owners who approve messages and answer buyer questions.
- Define a qualified meeting through account fit, relevant attendee, acknowledged problem, shared purpose, evidence requested and a specific next commitment.
- Confirm ownership of domains, mailboxes, contact data, suppression records, media accounts, content, analytics, CRM history and the clean exit route.
- Run a contained first phase and review rejected accounts, message objections, attendance, sales acceptance and lost opportunities before expanding.
Record the decision about cybersecurity lead generation agencies in the campaign brief so the team can revisit it when evidence changes. Keep a dated change log so rules, features and assumptions can be reviewed without rebuilding the whole motion.
Which mistakes distort decisions about cybersecurity lead generation agencies?
Selection risk around cybersecurity lead generation agencies usually appears when a polished feature list replaces a real workflow test. Make the following failure modes visible before migration, procurement or a longer commitment.
- Using cybersecurity as a single market without naming the product category, buyer environment and problem boundary.
- Treating demand generation, lead generation and appointment setting as interchangeable proposals.
- Letting an agency simplify technical claims without an accountable product or security review owner.
- Measuring booked meetings while attendance, sales acceptance, evidence requested and opportunity creation remain undefined.
- Accepting intent or technographic signals without a source, date, relevance test and human review.
- Hiring a growth provider when the actual constraint is product evidence, security assurance, implementation capacity or sales follow through.
Product capabilities and policies affecting cybersecurity lead generation agencies change. Verify the current documentation, run a contained test and judge the result against your own workflow before committing.
How should teams measure progress with cybersecurity lead generation agencies?
Measure the route from an approved account to an accepted commercial outcome. Record source verified accounts, relevant replies, qualified conversations, attended meetings, evidence requests, sales accepted opportunities, pipeline created, stage conversion, time to response and rejection reasons. Review by security category, company segment, buyer role, trigger and message. For demand work, connect visibility and engagement with later account activity. For outbound work, connect delivery and replies with accepted pipeline. Activity explains the result but does not replace it.
Compare the result with the assumptions in the brief, not with a generic internet benchmark. Keep the useful parts, revise one weak variable at a time and stop if the evidence or compliance position is unclear. For adjacent guidance, read The Best B2B Lead Generation Agencies in 2026, Compared by Delivery Model and Best B2B SaaS Demand Generation Agencies in 2026, then return to the Go to Market hub for the complete cluster.
Where can Provena support work involving cybersecurity lead generation agencies?
Provena fits B2B cybersecurity software and services companies that can define a finite buyer market and want research, verified data, cold email, LinkedIn, organic content, conversion and reply qualification under one operating owner. It is not a consumer lead marketplace, a phone only call centre, a security testing provider or a substitute for product, legal, compliance, security and sales ownership. Discovery should confirm that boundary before a programme is proposed. For cybersecurity lead generation agencies, Provena builds the research, data, messaging and operating loop around the chosen route. The goal is not more activity for its own sake. It is a controlled system that creates relevant conversations and shows clearly what should change next. See the B2B SaaS lead generation service and review Provena case studies before deciding whether support is appropriate.
Which sources should guide a shortlist for cybersecurity lead generation agencies?
Provider scope uses current first party service pages reviewed on 28 August 2026. Each provider controls its own claims and can change its services. Comparative fit, the selection scorecard and buyer controls are independent Provena editorial analysis. The primary references used for this article are Callbox cybersecurity lead generation service, Martal Group security lead generation service, SalesHive cybersecurity lead generation service, CyberTheory cybersecurity demand generation service, Provena B2B SaaS lead generation service, NIST Cybersecurity Framework, FTC CAN SPAM compliance guide, Google email sender guidelines, last reviewed on 15 September 2026. This guide is desk research on Callbox, Martal Group and the other options from those materials, not a hands-on trial of each; where Provena has run a cybersecurity lead generation agencies workflow itself, it says so. Reopen each reference before a material decision.
Frequently asked questions
What do cybersecurity lead generation services include?+
Depending on the provider, cybersecurity lead generation services include account research, contact data, cold email, LinkedIn outreach, SDR calling, paid and media demand, intent data and appointment setting. Callbox publishes a multichannel cybersecurity programme, Martal combines outsourced prospecting with appointment setting, SalesHive centres United States SDR calling and email, CyberTheory builds demand through paid, media and account based programmes, and Provena runs research, verified data, outreach, content and reply qualification as one system.
Which lead generation agency should a cybersecurity company use?+
Choose by the function you are missing. If you have demand but no one to work it, a calling and email appointment setter fits. If you have no demand, a media and account based programme or a full system fits. If you have both but no proof, fix the evidence before hiring anyone. Then confirm the agency can speak to security buyers without exaggeration, because a CISO who catches one inflated claim ends the conversation.
How do you generate leads for a cybersecurity company without sounding like every other vendor?+
Lead with a specific, verifiable observation about the buyer's environment or obligations, name the control or framework outcome you affect, and offer evidence rather than a demo. Security buyers respond to precision and to peers. Referencing a recognised framework such as the NIST Cybersecurity Framework, a published customer result and a clear scope boundary does more than any subject line.
Which risk should teams watch with cybersecurity lead generation agencies?+
Two, for cybersecurity lead generation agencies. First: Using cybersecurity as a single market without naming the product category, buyer environment and problem boundary. Second: Treating demand generation, lead generation and appointment setting as interchangeable proposals.
How can Provena support work around cybersecurity lead generation agencies?+
Provena fits B2B cybersecurity software and services companies that can define a finite buyer market and want research, verified data, cold email, LinkedIn, organic content, conversion and reply qualification under one operating owner. It is not a consumer lead marketplace, a phone only call centre, a security testing provider or a substitute for product, legal, compliance, security and sales ownership. Discovery should confirm that boundary before a programme is proposed. For work on cybersecurity lead generation agencies, review Provena's B2B SaaS lead generation service and confirm fit in a conversation before choosing support.